# PIS Consent Management and One-Off Domestic Payments Tutorial
source: https://developer.mastercard.com/open-banking-connect/documentation/tutorials-and-guides/consent-pis-tutorial/index.md
In this tutorial we sho how to get a list of available banks, request and obtain consent on behalf of a user, initiate one-off payments, and get the payment's status from a customer's bank.
Tip: Additionally we show how to perform one-off payments using Rest API and Java library. Note: SEPA and Cross-border payments are similar to Domestic payments. See the SEPA and Cross-border documentation for more information.
## What is Consent? {#what-is-consent}
With the introduction of PSD2 banks are now required to share customer data with third party providers (TPPs), while also requiring that sensitive customer data is shared securely. In order to ensure that only data which the customer has given explicit consent for is shared with the TPP, the customer must give consent to the ASPSP in a process called consent management. Open Banking Connect provides a consent management service for the TPP developer, described in the following tutorial for making a domestic payment.
### Consent and Open Banking Connect {#consent-and-open-banking-connect}
Open Banking Connect provides single universal API for the TPP developer so that they can connect to banks using all of the standards available across Europe. Currently supported standards include CMA9, PolishAPI, NextGenPSD2, STET, Czech Open Banking Standard, Slovak Banking API Standard, and Budapest Bank. Before a bank allows accessing any sensitive user information, first consent must be authorized by Open Banking Connect as described in this tutorial.
## Get List of available banks {#get-list-of-available-banks}
In order to make a one-off payment, the first step is to retrieve a list of available banks the customer is able to access. In this step we demonstrate how to fetch a list of available banks. See also the [Get List of ASPSPs documentation](https://developer.mastercard.com/open-banking-connect/documentation/pisfeatures/pis-get-list-of-aspsps/index.md).
The following sequence diagram shows the flows used to retrieve the list of available banks.
Diagram pis_list_of_banks
### Code sample {#code-sample}
To get a list of available banks submit the following request. The `returnAdditionalData` field is optional, and is used to return a list of capabilities for each Bank:
* Json
* Java
```json
POST /payments/aspsp
{
"requestInfo":{
"xRequestId":"123e4567-e89b-12d3-a456-426655440000"
},
"returnAdditionalData":[
"capabilities"
]
}
```
```java
import com.mastercard.openbanking.pisp.ApiClient;
import com.mastercard.openbanking.pisp.ApiException;
import com.mastercard.openbanking.pisp.Configuration;
import com.mastercard.openbanking.pisp.models.*;
import com.mastercard.openbanking.pisp.api.AspsPsApi;
public class Example {
public static void main(String[] args) {
ApiClient defaultClient = Configuration.getDefaultApiClient();
defaultClient.setBasePath("http://localhost/api");
AspsPsApi apiInstance = new AspsPsApi(defaultClient);
PostAspspsParamsBody body = new PostAspspsParamsBody(); // PostAspspsParamsBody | Request Body
try {
PostAspspsOKBody result = apiInstance.paymentsAspspsPost(body);
System.out.println(result);
} catch (ApiException e) {
System.err.println("Exception when calling AspsPsApi#paymentsAspspsPost");
System.err.println("Status code: " + e.getCode());
System.err.println("Reason: " + e.getResponseBody());
System.err.println("Response headers: " + e.getResponseHeaders());
e.printStackTrace();
}
}
}
```
Note: Do not change`xRequestId`, otherwise the request will not provide the pre-defined response in the Sandbox environment.
The below response with list of available banks will be received:
* JSON
```JSON
{
"originalRequestInfo":{
"xRequestId":"123e4567-e89b-12d3-a456-426655440000"
},
"aspsps":[
{
"id":"420e5cff-0e2a-4156-991a-f6eeef0478cf",
"name":"Sandbox ASPSP 1",
"aspspServices":[
"PIS",
"AIS",
"COF"
],
"profile":"CMA9",
"country":"GB",
"capabilities":{
"obtain_raw_consent_pis":true,
"retrieve_crossborder_pi_status":true,
"initiate_crossborder_payment":true,
"obtain_domestic_consent":true,
"obtain_ais_consent":true,
"retrieve_transactions":true,
"retrieve_accounts":true,
"delete_ais_consent":true,
"obtain_crossborder_consent":true,
"retrieve_balances":true,
"retrieve_account_details":true,
"retrieve_domestic_pi_status":true,
"obtain_raw_consent":true,
"initiate_domestic_payment":true
}
},
{
"id":"b806ae68-a45b-49d6-b25a-69fdb81dede6",
"name":"Sandbox ASPSP 2",
"aspspServices":[
"PIS",
"AIS",
"COF"
],
"profile":"PolishAPI",
"country":"PL",
"capabilities":{
"retrieve_transaction_details":true,
"obtain_sepa_consent":true,
"retrieve_crossborder_pi_status":true,
"initiate_crossborder_payment":true,
"obtain_domestic_consent":true,
"obtain_ais_consent":true,
"retrieve_transactions":true,
"retrieve_sepa_pi_status":true,
"initiate_sepa_payment":true,
"retrieve_accounts":true,
"delete_ais_consent":true,
"obtain_crossborder_consent":true,
"retrieve_balances":true,
"retrieve_account_details":true,
"retrieve_domestic_pi_status":true,
"initiate_domestic_payment":true
}
},
{
"id":"6bc896b5-1b5a-473a-a1d8-dfd3cbb4fab5",
"name":"Sandbox ASPSP 3",
"aspspServices":[
"PIS",
"AIS"
],
"profile":"NextGenPSD2",
"country":"NL",
"capabilities":{
"retrieve_sepa_pi_status":true,
"initiate_sepa_payment":true,
"retrieve_transaction_details":true,
"retrieve_accounts":true,
"delete_ais_consent":true,
"obtain_sepa_consent":true,
"retrieve_balances":true,
"obtain_ais_consent":true,
"retrieve_account_details":true,
"retrieve_transactions":true
}
},
{
"id":"08475b1c-5f59-48f7-8c62-dcfd8928dad2",
"name":"Sandbox ASPSP 4",
"aspspServices":[
"PIS",
"AIS"
],
"profile":"STET",
"country":"IT",
"capabilities":{
"retrieve_sepa_pi_status":true,
"initiate_sepa_payment":true,
"retrieve_transaction_details":true,
"retrieve_accounts":true,
"delete_ais_consent":true,
"obtain_sepa_consent":true,
"retrieve_balances":true,
"obtain_ais_consent":true,
"retrieve_account_details":true,
"retrieve_transactions":true
}
},
{
"id":"51e7e74c-a7e9-4402-b324-c132a225a878",
"name":"Wood Bank",
"aspspServices":[
"AIS",
"COF",
"PIS"
],
"profile":"CMA9",
"country":"GB",
"capabilities":{
"obtain_raw_consent_pis":true,
"retrieve_crossborder_pi_status":true,
"initiate_crossborder_payment":true,
"obtain_domestic_consent":true,
"obtain_ais_consent":true,
"retrieve_transactions":true,
"retrieve_accounts":true,
"delete_ais_consent":true,
"obtain_crossborder_consent":true,
"retrieve_balances":true,
"retrieve_account_details":true,
"retrieve_domestic_pi_status":true,
"obtain_raw_consent":true,
"initiate_domestic_payment":true
}
}
]
}
```
Note: In production environment, your application will have to redirect the user to the URI received in `scaRedirect` to complete the authentication with the bank and authorization of the consent.
## PIS Submit consent {#pis-submit-consent}
In this step you will learn how to submit payment services consent on behalf of the user.
After completing [Step 2](https://developer.mastercard.com/open-banking-connect/documentation/tutorials-and-guides/consent-pis-tutorial/index.md) where you learned how to get a list of available banks, the user logs into their bank and authorizes payment services.
In order to achieve this we leverage the Submit Consent endpoint in the API. See also the [Domestic Payment Initiation Consent documentation](https://developer.mastercard.com/open-banking-connect/documentation/pisfeatures/payment-initiation-consent-request/index.md).
The following sequence diagram shows the flow used to initiate the creation of consent for the one off payment.
Diagram pis_submit_consent
### Code sample {#code-sample-1}
To initiate consent request, submit the following request:
* JSON
* Java
```JSON
POST /payments/domestic-credit-transfers/consents
{
"requestInfo":{
"xRequestId":"123e4567-e89b-12d3-a456-426655440000",
"tppRedirectURI":"https://auth.dev.token.io/callback",
"aspspId":"51e7e74c-a7e9-4402-b324-c132a225a878",
"merchant":{
"id":"MerchantId",
"name":"MerchantName"
},
"flags":[
"Return.Raw.Consent"
]
},
"payments":{
"endToEndIdentification":"Notification",
"localInstrument":"UK.FasterPayments",
"instructedAmount":{
"currency":"GBP",
"amount":100.23
},
"creditorAccount":{
"schemeName":"UK.AccountNumber",
"identification":"30087236"
},
"creditorAgent":{
"clearingSystemIdentification":"UK.SortCode",
"memberIdentification":"283746"
},
"creditorName":"Wood bank",
"creditorAddress":{
"street":"Street",
"buildingNumber":"15",
"city":"City",
"postalCode":"PostCode",
"countrySubDivision":"Division",
"country":"CC"
},
"remittanceInformationUnstructured":"Payment for fruits",
"requestedExecutionDate":"2020-03-25",
"remittanceInformationReference":"UniqueRef1"
}
}
```
```java
import com.mastercard.openbanking.pisp.ApiClient;
import com.mastercard.openbanking.pisp.ApiException;
import com.mastercard.openbanking.pisp.Configuration;
import com.mastercard.openbanking.pisp.models.*;
import com.mastercard.openbanking.pisp.api.DomesticPaymentsConsentApi;
public class Example {
public static void main(String[] args) {
ApiClient defaultClient = Configuration.getDefaultApiClient();
defaultClient.setBasePath("http://localhost/api");
DomesticPaymentsConsentApi apiInstance = new DomesticPaymentsConsentApi(defaultClient);
PostPaymentsDomesticCreditTransfersConsentsParamsBody body = new PostPaymentsDomesticCreditTransfersConsentsParamsBody(); // PostPaymentsDomesticCreditTransfersConsentsParamsBody | Domestic Payment consent to be wired through Faster Payment System
try {
PostPaymentsDomesticCreditTransfersConsentsOKBody result = apiInstance.paymentsDomesticCreditTransfersConsentsPost(body);
System.out.println(result);
} catch (ApiException e) {
System.err.println("Exception when calling DomesticPaymentsConsentApi#paymentsDomesticCreditTransfersConsentsPost");
System.err.println("Status code: " + e.getCode());
System.err.println("Reason: " + e.getResponseBody());
System.err.println("Response headers: " + e.getResponseHeaders());
e.printStackTrace();
}
}
}
```
Note: Do not change `aspspId`, `localInstrument`, `currency`, `amount`, `schemeName`, `identification`, `clearingSystemIdentification`, `memberIdentification`, and `creditorName`, otherwise the request will not provide the pre-defined response in the Sandbox environment.
The following is an example of a received response. The User should be redirected to the link from the `scaRedirect` field, and prompted to authorize consent with the Bank. Once authorized, the consent will last for the duration of the payment transaction:
* JSON
```JSON
{
"originalRequestInfo": {
"xRequestId": "123e4567-e89b-12d3-a456-426655440000"
},
"aspspSCAApproach": "REDIRECT",
"consentRequestId": "dc3c7a99-dacc-4ce6-9c97-4bd812a7a44a",
"_links": {
"scaRedirect": "https://fank.sandbox.token.io/cma9/authorize?response_type=code%20id_token&client_id=wood-client&redirect_uri=https%3A%2F%2Fauth.dev.token.io%2Fcallback&scope=openid+payments&state=tokenio-state__rq-3fNyxLHmxcZjAkCQuhsJAVF8R4Hw-5zKtXEAq__&request=eyJraWQiOiJJOW8xR25mQloya2xINlpVZTY2QksweWRaa2siLCJhbGciOiJSUzI1NiJ9.eyJzdWIiOiJjNjBiYjZiMzYzMWQ0N2RhYTEzYTc3ZGVmMDBlOTI2NyIsImlzcyI6Indvb2QtY2xpZW50IiwicmVzcG9uc2VfdHlwZSI6ImNvZGUgaWRfdG9rZW4iLCJub25jZSI6Ijk4MWUwODZhLTZkZGMtNDVlZi1hMmM5LWM2NWZiYTdiM2U4MSIsImNsaWVudF9pZCI6Indvb2QtY2xpZW50IiwiYXVkIjoiaHR0cHM6XC9cL2Zhbmsuc2FuZGJveC50b2tlbi5pb1wvY21hOVwvIiwic2NvcGUiOiJvcGVuaWQgcGF5bWVudHMiLCJjbGFpbXMiOnsiaWRfdG9rZW4iOnsib3BlbmJhbmtpbmdfaW50ZW50X2lkIjp7ImVzc2VudGlhbCI6dHJ1ZSwidmFsdWUiOiJjNjBiYjZiMzYzMWQ0N2RhYTEzYTc3ZGVmMDBlOTI2NyJ9LCJhY3IiOnsiZXNzZW50aWFsIjpmYWxzZSwidmFsdWUiOiJ1cm46b3BlbmJhbmtpbmc6cHNkMjpjYSJ9fX0sInJlZGlyZWN0X3VyaSI6Imh0dHBzOlwvXC9hdXRoLmRldi50b2tlbi5pb1wvY2FsbGJhY2siLCJzdGF0ZSI6InRva2VuaW8tc3RhdGVfX3JxLTNmTnl4TEhteGNaakFrQ1F1aHNKQVZGOFI0SHctNXpLdFhFQXFfXyIsImV4cCI6MTU4NTE1MTQ0NiwiaWF0IjoxNTg1MTQ4NDQ2LCJqdGkiOiIwOTQzMjM3My1jOTJkLTQ3ZjEtYmNiNC1jZDhhMDA0YThkMzYifQ.LCD9apKMNhrH47XOj7Yy2Kski0GsZRQUi5I-zSPFeT-qpIxhbnXr48S8UZMewkNDlvvW7tsKGL-TUDcSxGcxtfpAGj0EtgKI1y81RRIj8h-1VUU-wRUjPilEjIXIW2Dn6jWLrb_QM-wAVv2HgeTaoEssc0OlwDA6dw-M9dKxO965DZd6kU3Rx6xVkrh-AVWpFqC22zDz9Phs1Oqzdzh7vkR0XuhIlfLZaW3lqRlT9VkW1Aeq9dxbcTZ3IrvMamOrTjCF223ta7ooyzQArQ-SthCDTOUhMFgNtk4UOjZJOG0AUmceS12lmAUyhFB843Nok7X6VDkcyL9DoMO1TJTCOQ&nonce=981e086a-6ddc-45ef-a2c9-c65fba7b3e81"
}
}
```
Note: In the Production environment, your application needs to redirect the User to the URI received in `scaRedirect` to complete the authentication with the Bank and authorization of the consent.
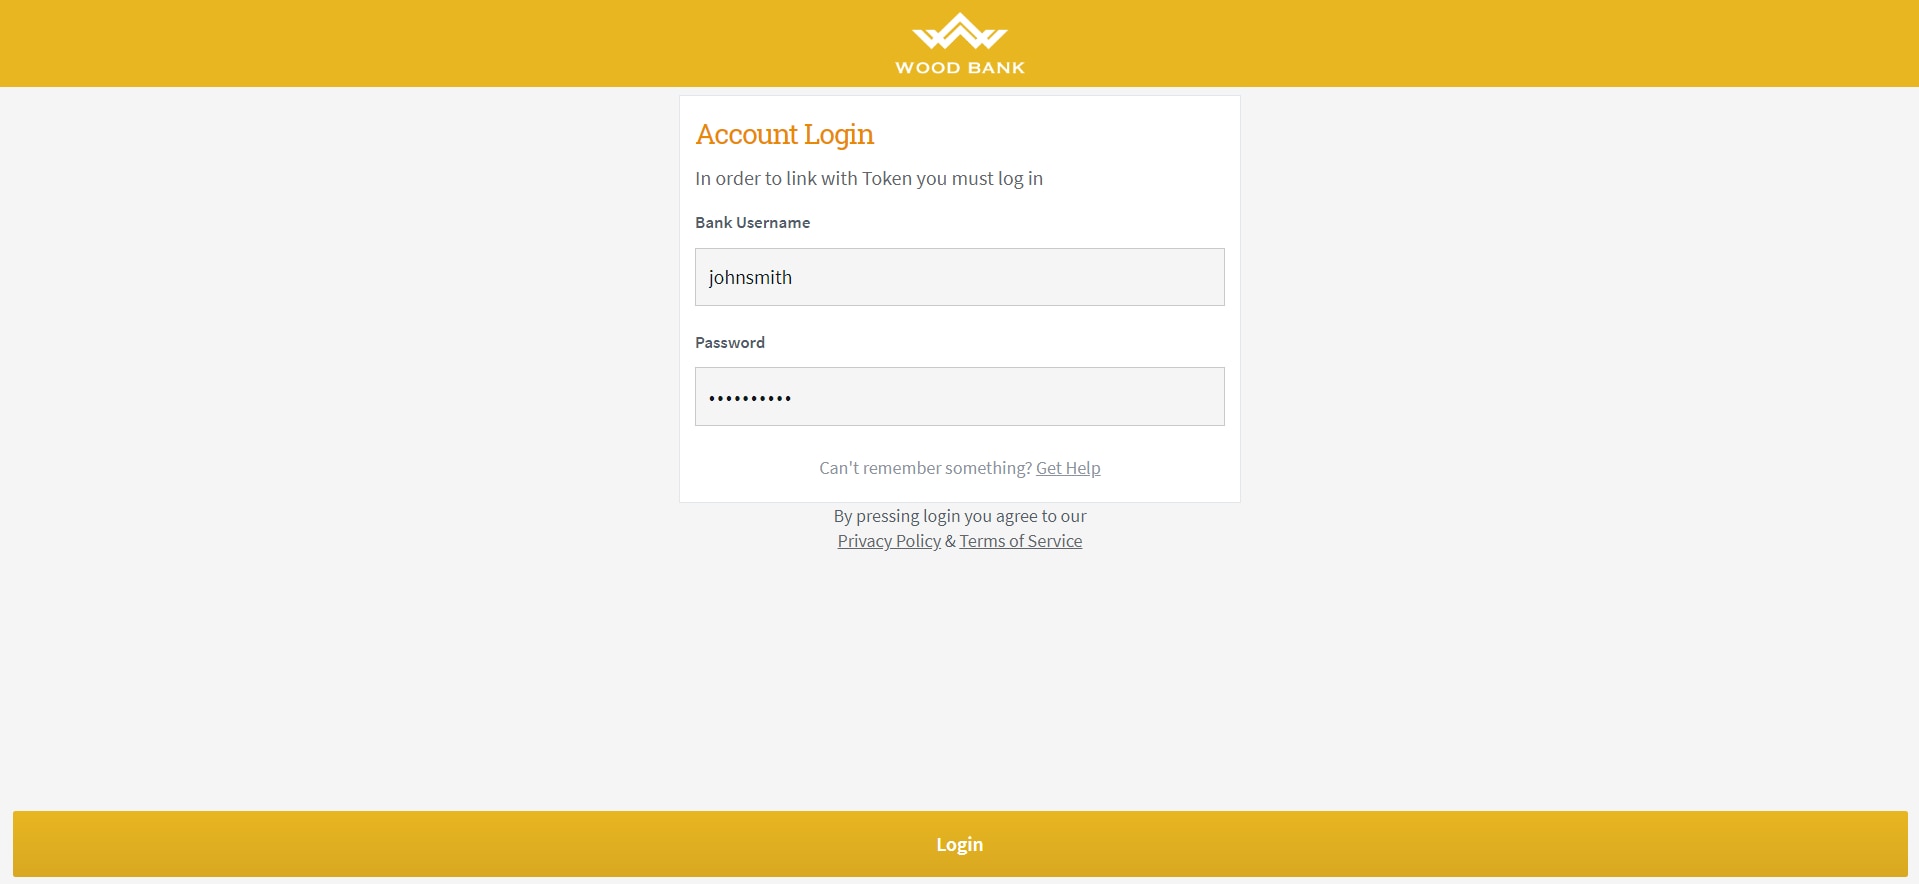
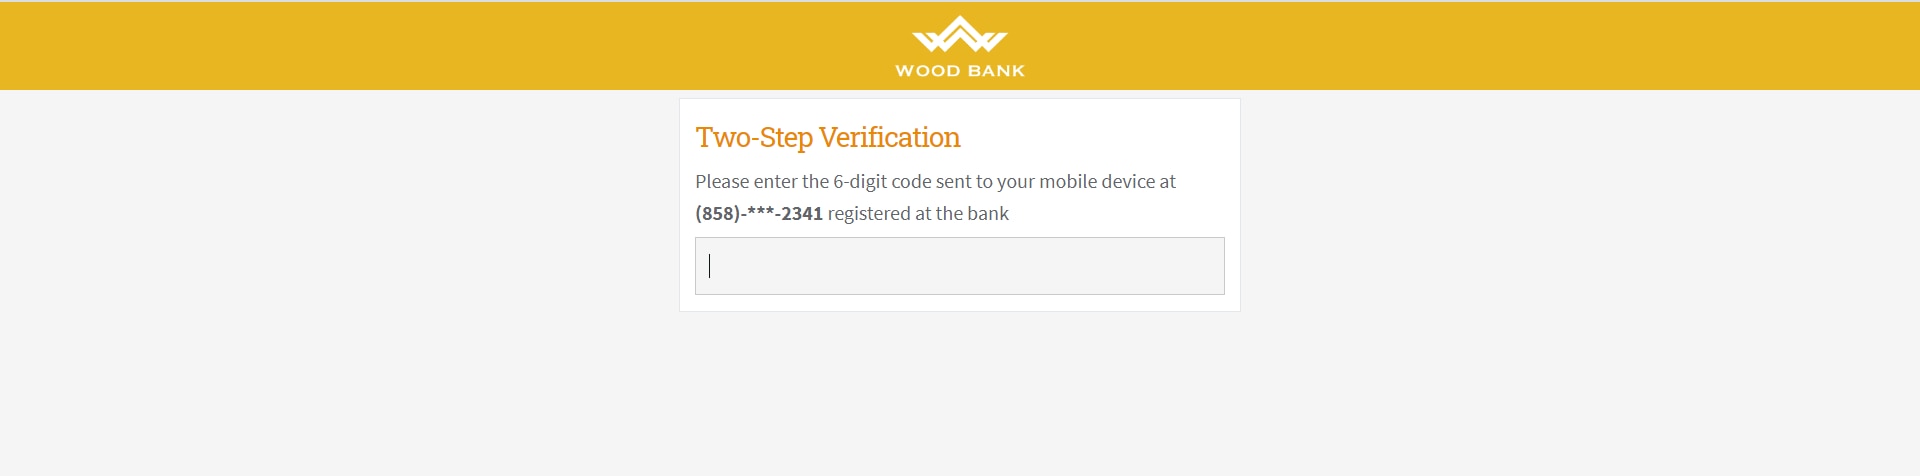
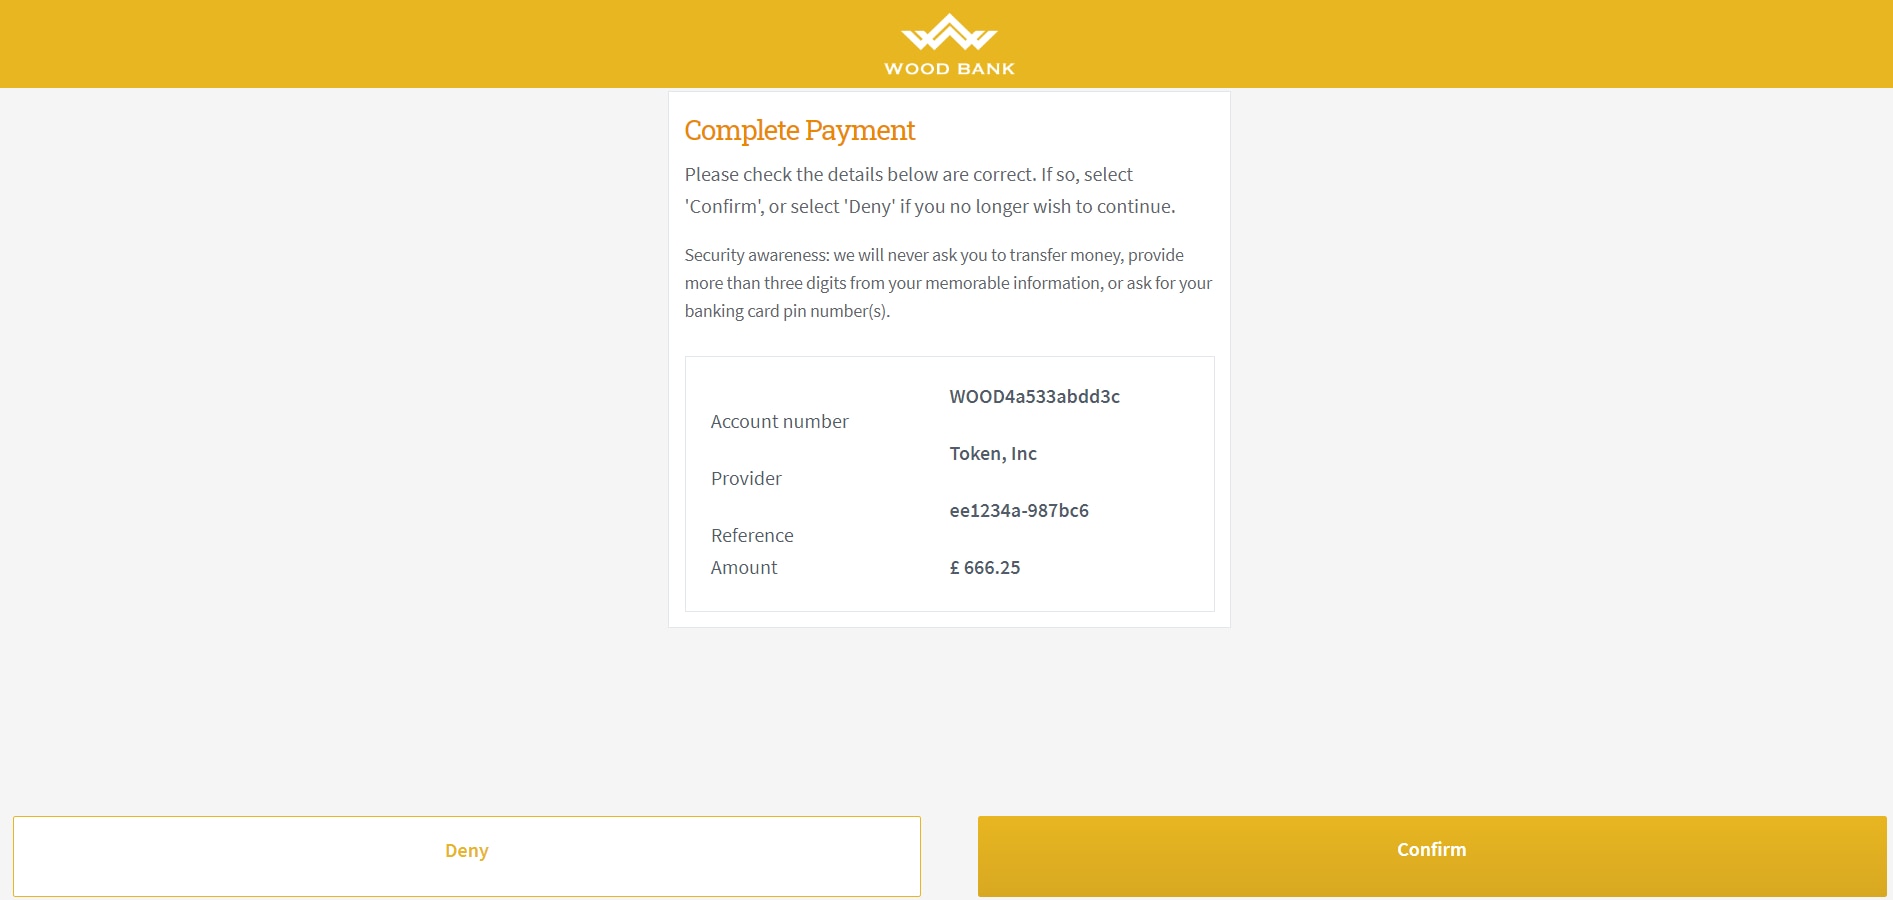
After your application redirects the User to the `scaRedirect`, the User authenticates with the bank to authorize consent. The above `scaRedirect` link allows access to a demo Bank application, which is completed as follows:
1. Click "Login" to login with the auto-filled credentials
2. Supply any 6 digits to complete two-factor authentication
3. Confirm payment request
4. Obtain callback with authorization string (this link is for display purposes and not functional)
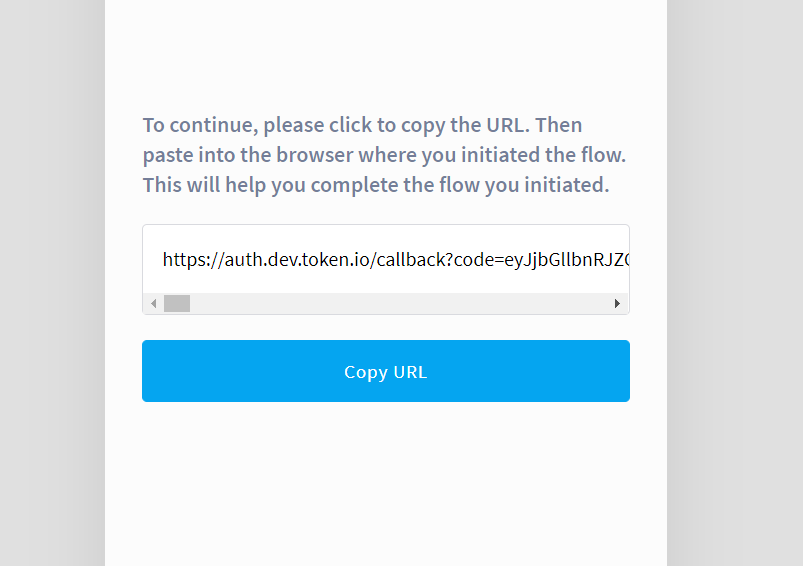
Tip: After the User authorizes consent, your application obtains an authorization string from auth query parameter on the URI address specified in the `tppRedirectURI` field in the request.
***The authorization string will timeout after a maximum period of 10 minutes. This may vary by bank but should not exceed 10 minutes.***
You application uses this authorization string (ex. `auth=123234234&state=FH888999`) in the Payment Credit Transfer Initiation Request endpoint below to get consentId and use it in all subsequent requests associated with the consent.
In the Sandbox environment, the authorization string and consentId are hardcoded (See the `authorization` and `consentId` fields in the respective request body).
Alert: The OBIE, in alignment with the security community, recommends the use of the Hybrid flow. The platform today enforces this by setting the initial response type to **code id_token** in the authorization request to the ASPSP's Authorization Server. The Authorization server is required to return both the access code and id_token in this case, but the manner in which it does this is left to the discretion of the Authorization Server. This could be in either form:
* TPP_REDIRECT_URL?All_Params
* TPP_REDIRECT_URL#All_Params
The current best practice is to return these values as a hash fragment. This allows the User Agent to receive the values and skip redirection (performance enhancement), and not send the access code through a query string parameter where it will be logged by proxies, firewalls, application servers, and other services in the application path. Having the access code logged in plain text would weaken its value.
For this reason, it is suggested the TPP application parse the access code from the hash fragment and POST it to the Client Service (TPP service) in an AJAX request, where the value may be safely ensconced within the POST body.
## Redeem one-off payment {#redeem-one-off-payment}
In this step we demonstrate how to redeem a one-off payment.
After successfully submitting User's consent request in [Step 3](https://developer.mastercard.com/open-banking-connect/documentation/tutorials-and-guides/consent-pis-tutorial/index.md), it is time to redeem the payment. This flow assumes the User has already consented to this access and the bank system stores this record of consent or `consentId`. See also the [Domestic Payment Initiation documentation](https://developer.mastercard.com/open-banking-connect/documentation/pisfeatures/payment-credit-transfer-initiation-request/index.md).
The following sequence diagram shows the flow used to initiate a one-off payment on the bank's side using an authorization string provided by the User.
Diagram redeem_payment
### Code sample {#code-sample-2}
To redeem the payment, submit the following request:
* JSON
* Java
```JSON
POST /payments/domestic-credit-transfers
{
"requestInfo": {
"xRequestId": "123e4567-e89b-12d3-a456-426655440000",
"authorization": "UKdpVsbG8gQ2TP9kZWJleft53serYXV0aUK001",
"aspspId": "420e5cff-0e2a-4156-991a-f6eeef0478cf",
"merchant": {
"id": "MerchantId",
"name": "MerchantName"
}
}
}
```
```java
import com.mastercard.openbanking.pisp.ApiClient;
import com.mastercard.openbanking.pisp.ApiException;
import com.mastercard.openbanking.pisp.Configuration;
import com.mastercard.openbanking.pisp.models.*;
import com.mastercard.openbanking.pisp.api.DomesticPaymentsApi;
public class Example {
public static void main(String[] args) {
ApiClient defaultClient = Configuration.getDefaultApiClient();
defaultClient.setBasePath("http://localhost/api");
DomesticPaymentsApi apiInstance = new DomesticPaymentsApi(defaultClient);
PostPaymentsDomesticCreditTransfersParamsBody body = new PostPaymentsDomesticCreditTransfersParamsBody(); // PostPaymentsDomesticCreditTransfersParamsBody | Request Body
try {
PostPaymentsDomesticCreditTransfersOKBody result = apiInstance.paymentsDomesticCreditTransfersPost(body);
System.out.println(result);
} catch (ApiException e) {
System.err.println("Exception when calling DomesticPaymentsApi#paymentsDomesticCreditTransfersPost");
System.err.println("Status code: " + e.getCode());
System.err.println("Reason: " + e.getResponseBody());
System.err.println("Response headers: " + e.getResponseHeaders());
e.printStackTrace();
}
}
}
```
Note: Do not change `authorization` and `aspspId`, otherwise the request will not provide the pre-defined response in the Sandbox environment.
The following is an example of a received response indicating the payment request was successful:
* JSON
```JSON
{
"originalRequestInfo": {
"xRequestId": "123e4567-e89b-12d3-a456-426655440000"
},
"transfer": {
"paymentId": "UK8aFR415:22Aa:6asdC",
"transactionStatus": "RCVD"
},
"consent": {
"consentRequestId": "12337",
"consentId": "UK8sPNznYtfV:5zKxyC"
}
}
```
Note: Use `consentId` in future requests related to this consent. Tip: As shown in the response above, `transactionStatus` with value `RCVD` indicates that the payment was received.
OB Connect uses the `paymentId` field to get a payment's status, covered in in the next step.
## Get Payment Status {#get-payment-status}
After submitting payment a customer may be interested in the status of this payment transaction. In this step we demonstrate how to get a payment transaction's status. See also the [Domestic Payment Transaction Status documentation](https://developer.mastercard.com/open-banking-connect/documentation/pisfeatures/get-payment-status-request/index.md).
Prerequisites: The customer/TPP needs to perform the following operations before executing the Get Payment Status call:
* `Submit Consent` operation to get the authorization string.
* `Submit Payment Initiation` operation to get the consentId.
The following sequence diagram shows the flow used to retrieve the payment status from the User's bank for the specified payment based on previously obtained consent.
Diagram get_payment_status
### Code sample {#code-sample-3}
To get the status of the payment transaction, submit the following request:
* JSON
* Java
```JSON
POST /payments/domestic-credit-transfers/payment-status
{
"paymentId": "UK8aFR415:22Aa:6asdC",
"requestInfo": {
"xRequestId": "123e4567-e89b-12d3-a456-426655440000",
"consentId": "UK8sPNznYtfV:5zKxyC",
"aspspId": "420e5cff-0e2a-4156-991a-f6eeef0478cf"
}
}
```
```java
import com.mastercard.openbanking.pisp.ApiClient;
import com.mastercard.openbanking.pisp.ApiException;
import com.mastercard.openbanking.pisp.Configuration;
import com.mastercard.openbanking.pisp.models.*;
import com.mastercard.openbanking.pisp.api.DomesticPaymentsStatusApi;
public class Example {
public static void main(String[] args) {
ApiClient defaultClient = Configuration.getDefaultApiClient();
defaultClient.setBasePath("http://localhost/api");
DomesticPaymentsStatusApi apiInstance = new DomesticPaymentsStatusApi(defaultClient);
PostPaymentsDomesticCreditTransfersPaymentStatusParamsBody body = new PostPaymentsDomesticCreditTransfersPaymentStatusParamsBody(); // PostPaymentsDomesticCreditTransfersPaymentStatusParamsBody | Request Body
try {
PostPaymentsDomesticCreditTransfersPaymentStatusOKBody result = apiInstance.paymentsDomesticCreditTransfersPaymentStatusPost(body);
System.out.println(result);
} catch (ApiException e) {
System.err.println("Exception when calling DomesticPaymentsStatusApi#paymentsDomesticCreditTransfersPaymentStatusPost");
System.err.println("Status code: " + e.getCode());
System.err.println("Reason: " + e.getResponseBody());
System.err.println("Response headers: " + e.getResponseHeaders());
e.printStackTrace();
}
}
}
```
Note: Do not change `paymentId`, `consentId`, and `aspspId`, otherwise the request will not provide the pre-defined response in the Sandbox environment.
The following received response is an example of the payment transaction's status:
* JSON
```JSON
{
"originalRequestInfo": {
"xRequestId": "123e4567-e89b-12d3-a456-426655440000"
},
"payments": {
"transactionStatus": "ACSC"
}
}
```
## Get Raw Consent {#get-raw-consent}
Depending on each specific bank Application requirements, some Applications may want to store the original consent information. Currently the use of Raw Consent is OBIE/CMA9 specific. See also the [PIS Get Raw Consent documentation](https://developer.mastercard.com/open-banking-connect/documentation/pisfeatures/pis-get-raw-consent/index.md).
Prerequisites: The customer/TPP needs to perform the following operations before executing the Get Raw Consent call:
* `Submit Consent Request` operation needed to get the Authorization string.
* `Submit Payment Request` operation needed to get consentId.
The following sequence diagram shows the flow used to retrieve raw consent from the Bank for the specified payment based on previously obtained consent.
Diagram get_raw_consent
### Code sample {#code-sample-4}
To get raw consent, submit the following request:
***POST /payments/consents/raw***
* JSON
```JSON
{
"requestInfo": {
"aspspId": "420e5cff-0e2a-4156-991a-f6eeef0478cf",
"xRequestId": "123e4567-e89b-12d3-a456-426655440000",
"consentId": "GFiTpF3:EBy5xGqQMatk"
}
}
```
Note: Do not change `aspspId` and `consentId`, otherwise the request will not provide the pre-defined response in the Sandbox environment.
The following received response is an example of the raw consent:
* JSON
```JSON
{
"originalRequestInfo": {
"xRequestId": "123e4567-e89b-12d3-a456-426655440000"
},
"rawConsent": "ewogIHNjb3BlOiBhY2NvdW50cywKICB0b2tlbl90eXBlOiBCZWFyZXIsCiAgYWNjZXNzX3Rva2VuOiBXMzRpVFhlVFZVZGtpRFpvVDlXVFVUMFE1eW5Hdk1uc3NXbUZ5bmMwVGlzY0ZlbEpiTWM0WmhTaXBHalRtNUd3dzVGSWs2TVVqeE9VeVV3TVp3UU1pSXlMMDNBZmpiU2RHekdWNGlpVHlpNmkwa3pkT05HMk1DaXd4WVVTYjNRaWt5OTRNT1dJc05SVG1GT0pYYnVjNU5paWkyMDAyWTJwVnk0VzVPajVKY1pZVzJSWVVNMjJZaU4ya1pZSlpVdGx0amJjM1hKV0FJbHZPV2lsSmJJbFljYko5TXRXT0lGMkFCWlZDalZjMFVJbiwKICByZWZyZXNoX3Rva2VuOiBDTzM0V01tV0c1TWl2V1NVWjAzT2M1cGVGYzVKbk1VVHdsTWlDYVlaYkc1azlGeUFRNElCOVdVWUxrYk9HU2N5VjB0VGMyMzNzazJ3MmZzNHlaWVpKMm5zd21pdHhpemNWaU1Oak5ZNkpqQXZSVVVKeTZieU9zSjBsSXVoVEcyV2RNaURsZGlWWjJrMFhaU2p3STR5TlZsVVdpalJqRlFPOXQ1TUl6eWNpNG41YnBZMlRKajAyRmJNTVhVWDNJYmlObVRZWW53VFdPR21PVFRJYmlHZWlvUXhqWldWSWMwMmlXQVVraUpDT2xjaSwKICBleHBpcmVzX2luOiAzNjAwCn0K"
}
```
Tip: For example, lets assume that your application is selling chairs.
1. A user enters the web shop page and adds items into the basket.
2. When they decide to pay for it through Open Banking (OBC) , your application creates a request to OBC payments/consent.
3. The response contains `scaRedirectUrl` and `consentRequestId`, your application needs to link (save) `consentRequestId` to the basked of the user (or user web session).
4. Then your application needs to redirect the user to the `scaRedirectUrl` .
5. A User following the link, gives consent at the Bank's side and your application is going to receive the token through Consent Redirect URL.
6. Your web application needs to extract the following information from Consent Redirect URL:
* consentId - ID used for credit transfer.
* consentRequestId - The same as received in the response for payments/consent API call. This way your application can find the basket where the consent was received.
## Common PIS error codes {#common-pis-error-codes}
When an error code is returned, the response body provides reason code and error description of the raised error. For a more comprehensive list see [Response and Error Codes](https://developer.mastercard.com/open-banking-connect/documentation/response-and-error-codes/index.md). Also check the individual PIS feature documentation page for specific error codes associated with that endpoint. Below is a list of possible error reason codes that can be returned, along with brief error descriptions:
| Reason Code | Error Description | Details | Scenario Details |
|----------------------------------|--------------------------------------------------------------------------------------------------|-----------------------------------------------------------------------------------------|----------------------------------------------------------------------------------------------------------------------------------------|
| `FORMAT_ERROR` | "Please find possible scenarios and messages in FORMAT ERROR tab" | "path\[i\]=;" where i = 0, 1, 2, and so on. for each element that failed the validation | Schema validation failure |
| `FORMAT_ERROR` | "One and only one instance of mutually exclusive fields should be populated" | "path\[i\]=;" where i = 0, 1, 2, and so on. for each element that failed the validation | Mutually exclusive fields |
| `INACTIVE_ACCOUNT` | n/a (not included in the response) | | TPP validation failure |
| `INACTIVE_PROVIDER` | n/a (not included in the response) | | ASPSP validation failure |
| `INACTIVE_URL` | n/a (not included in the response) | | TPP redirect URL not whitelisted |
| `FORMAT_ERROR` | \[Path '/limit'\] Numeric instance is lower than the required minimum (minimum: , found: ) | "path\[i\]=;" where i = 0, 1, 2, and so on. for each element that failed the validation | Get Account Transactions limit \< 1 |
| `MAX_LIMIT_FORMAT_ERROR` | "\[Path '/limit'\] Numeric instance is greater than the accepted maximum (maximum: , found: )" | "path\[i\]=;" where i = 0, 1, 2, and so on. for each element that failed the validation | Get Account Transactions limit \> MAX |
| `PROVIDER_ERROR` | "Unable to process request this time." | | Error returned from Connectivity Partner |
| `NOT_FOUND` | "Method not supported by Provider's API profile" | | Method not supported by ASPSP |
| `INVALID_TOKEN` | n/a (not included in the response) | | Invalid Token |
| `NOT_FOUND` | "Method not support by Provider's API profile" | "path\[i\]=;" where i = 0, 1, 2, and so on, for each element that failed the validation | Failed to provide a supported localInstrument in PI Consent |
| `FORMAT_ERROR` | "Payment details are not aligned with selected localInstrument" | "path\[i\]=;" where i = 0, 1, 2, and so on, each element that failed the validation | Failed to provide required details for selected localInstrument in PI consent |
| `FORMAT_ERROR` | "Execution Date cannot be in the past" | "path\[i\]=;" where i = 0, 1, 2, and so on, for each element that failed the validation | Requested Execution Date is in the past |
| `DATEFROM_GREATER_THAN_DATETO` | "bookigDateFrom cannot be greater than bookingDateTo" | "path\[i\]=;" where i = 0, 1, 2, and so on, for each element that failed the validation | bookigDateFrom is greater than bookingDateTo |
| `INVALID_DATEFROM_OR_DATETO` | "bookigDateFrom and/or bookingDateTo should be a valid date or cannot be a date from the future" | "path\[i\]=;" where i = 0, 1, 2, and so on, for each element that failed the validation | invalid date for bookigDateFrom and/or bookingDateTo (for example, 2019-15-31; 0123-00-3; 2019-00-31 and so on, or a date from future) |
| `FORMAT_ERROR` | "bookingDateFrom and /or bookingDateTo should be in ISO Date format (for example, 2019-10-25)" | "path\[i\]=;" where i = 0, 1, 2, and so on, for each element that failed the validation | bookingDateFrom and /or bookingDateTo not ISO Date format |
| `INVALID_PAYMENT_AMOUNT` | "Payment amount should be greater than zero" | Return as path to the element that failed the validation | Payment amount is less or equal to zero, at payment initiation |
| `STARTDATE_GREATER_THAN_ENDDATE` | "End date is lower than start date" | Return as path to the element that failed the validation | startDate is greater than endDate |
| `INVALID_STARTDATE_OR_ENDDATE` | "startDate and/or endDate cannot be a date from the past" | Return as path to the element that failed the validation | startDate or endDate is from past |
| `FORMAT_ERROR` | "startDate and /or endDate should be in ISO Date format (for example, 2019-10-25)" | Return as path to the element that failed the validation | startDate or endDate is not in ISO format |
| `UNCLEAR_PAYMENT_INSTRUCTION` | "It is unclear what payment is requested - Future Dated or Standing Order. " | Return as path to the element that failed the validation | Both Standing Order and Future Date fields are populated. |
| `INVALID_INPUT` | "Invalid or missing input" | Return as path to the element that failed the validation | empty From/To fields or invalid input for From/To/Cc Onboarding Mailboxes |
| `NOT_ALLOWED` | "You are not allowed to perform request to this ASPSP" | Return as path to the element that failed the validation | TPP not allowed to perform request to this ASPSP |
| `NOT_ALLOWED` | "You are not allowed to perform this request to this ASPSP" | Return as path to the element that failed the validation | TPP not allowed to perform PIS or AIS request to ASPSP |